The Unified
Cybersecurity Platform
One Agent | One Console | One Security Operating Picture.
Security has become fragmented across too many tools, consoles and disconnected sources. Sec INCYTE brings it together — giving security and IT teams one place to see what is happening, understand why it matters and take action.
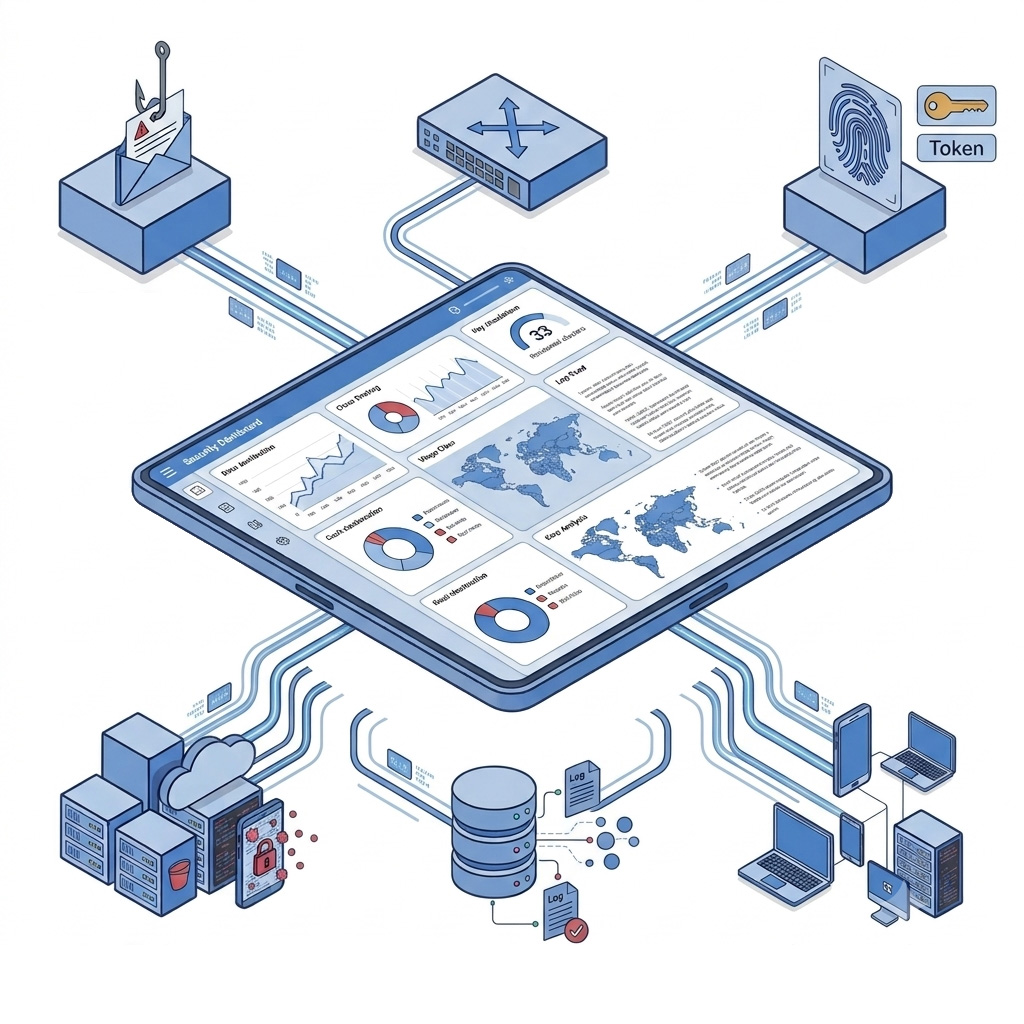
One lightweight agent + agentless coverage
20+ integrated capability areas
SaaS, hybrid and on-premises
Cybersecurity has become too fragmented to manage.
The challenge isn’t having too little security. It’s managing too much of it.
Teams often operate separate tools for privileged access, SIEM, endpoint security, vulnerability management, monitoring, asset management, automation, backups and service operations. The result is more consoles, more hand-offs and less context when it matters most.
Bring security operations together.
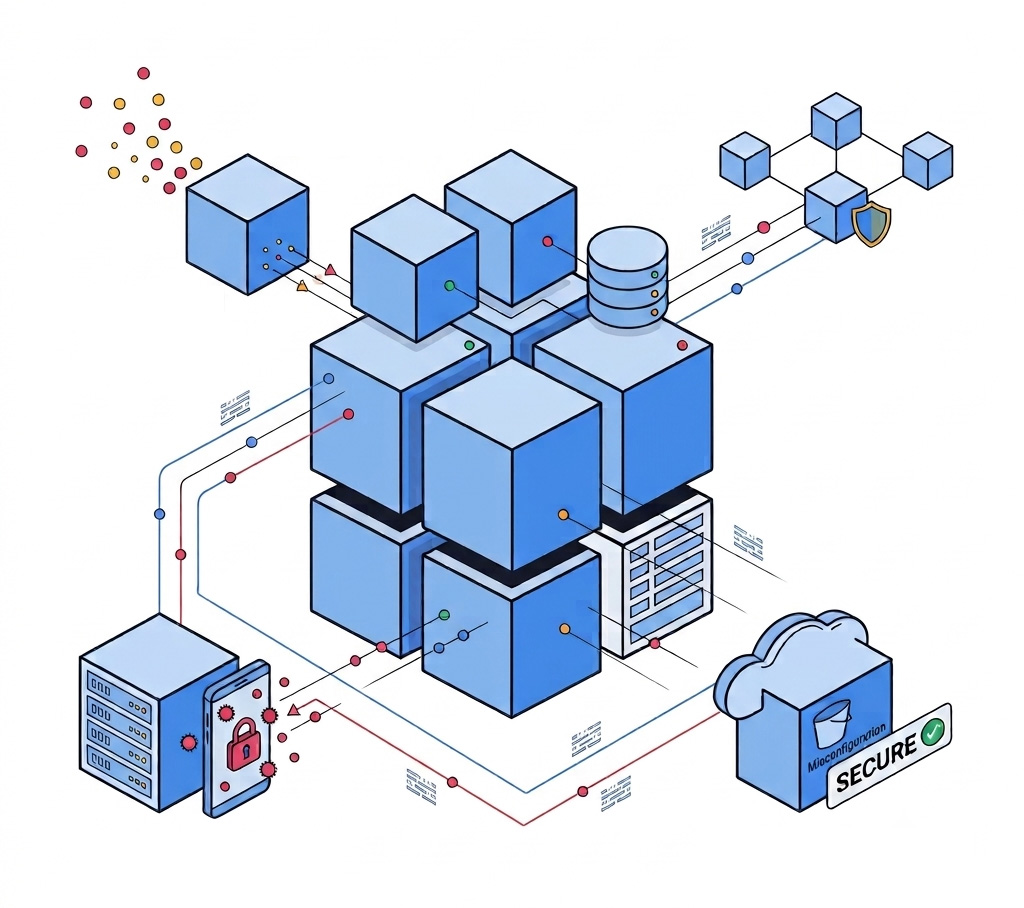
Sec INCYTE connects telemetry, security controls, exposure management, investigation and remediation through one platform. Instead of moving between disconnected tools, teams can move from signal to context, from context to intelligence and from intelligence to action.

One Agent. Many Security Functions.
Deploy one lightweight agent on Linux and Windows endpoints and enable the capabilities you need centrally. For infrastructure that cannot run an agent, Sec INCYTE extends coverage through agentless SNMP, SSH and Redfish access.
From Signal to Insight. From Insight to Action.
Sec INCYTE brings together data from endpoints, networks, cloud, identity, email, applications and infrastructure. It correlates that information with asset, vulnerability, behavioural and threat context so teams can investigate and act from the same operating picture.
01
COLLECT
Gather endpoint, network, cloud, identity, email and infrastructure telemetry.
02
CORRELATE
Connect related events, assets, users, vulnerabilities and behaviours.
03
PRIORITIZE
Turn noise into meaningful findings and incidents.
04
RESPOND
Investigate, contain, remediate and automate from the same console.
05
ASSURE
Maintain auditability, posture, backups, hardening and operational visibility.
Four Platform Pillars
Identity & Access Governance
Threat Detection & Exposure
Infrastructure & Operational Resilience
Workforce & Human Risk Intelligence
Find the Exposure Before the Attacker Does
Sec INCYTE brings vulnerability assessment, penetration testing and exposure management into the same platform used for security operations. Define targets, scan across multiple attack surfaces, prioritize findings and verify remediation without losing operational context.
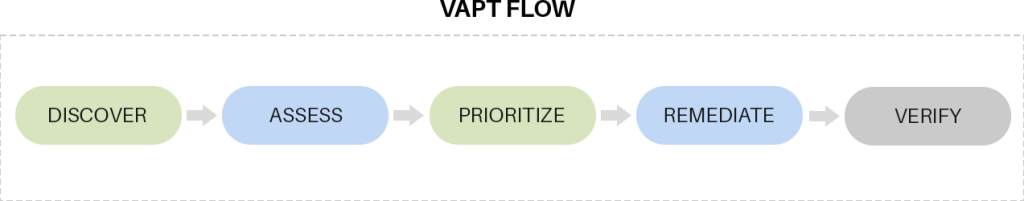
Nine attack-surface domains
Network Infrastructure • Web / DAST • API Security • SAST • Container / Kubernetes • Attack Surface Management • Mobile • Active Directory / Identity • Cloud / CSPM
Highlights
Multi-tool scanner engine • Tenable One ACR scoring • Crown Jewel alerts • live scan terminal • 1-click Verify Patch • CERT-In reporting
Ask Your Security Environment. Then Act
Sec INCYTE uses AI where it can reduce investigation and operational effort — not as a generic label. Teams can ask plain-English questions about their environment, receive AI-assisted diagnosis and use conversational automation with explicit permission controls.
Examples
AI control
Automation sessions can run in Read-only or Actionable mode, with permission gating, history and export.
See the Connections Behind the Alert.
Go beyond endpoint alerts with live and historical network visibility. Sec INCYTE combines NetFlow, collector flows, firewall telemetry, bandwidth analysis, live packet capture and connection history to help investigators understand how systems communicate and how lateral movement may have progressed.
Secure Cloud Workloads Without Creating Another Security Silo.
Use the same Sec INCYTE agent across cloud VMs and on-premises workloads. Add cloud posture assessment through the VAPT engine, cloud log-source coverage, backup and automation — all within the same operating model.
Works With the Technology You Already Run.
Sec INCYTE is designed for mixed, real-world environments. More than 120 decoder and rule families provide coverage across endpoint operating systems, network and firewall platforms, cloud and containers, email, virtualization, identity, security products, web and middleware, databases, collaboration systems, VoIP and agent telemetry.
Security Without Losing Control.
Sec INCYTE is built for accountable operations. Multi-tenancy, data isolation, RBAC, delegation, central approvals and an append-only audit trail help organisations maintain control over security actions and sensitive access.
Make Security Simpler
Bring visibility, protection, investigation and response together in one cybersecurity platform.